

Cisco has patched another actively exploited zero-day flaw in its Secure Email Gateway (SEG) that lets remote unauthenticated attackers execute commands with root privileges.
Tracked as CVE-2026-76519, this vulnerability stems from a relative path traversal weakness in SEG’s Advanced Malware Protection (AMP) feature, caused by improper handling of email attachments. Threat actors can exploit this issue by sending an email with a maliciously crafted attachment through an unpatched device.
“A successful exploit could allow the attacker to write arbitrary files and execute commands with root privileges on the underlying operating system,” Cisco said in a Wednesday advisory. “In October 2026, the Cisco PSIRT became aware of active exploitation of this vulnerability.”
CVE-2026-76519 affects SEG instances where the File Reputation service is enabled and assigned to a mail policy, and the Content Scanner Tools version is earlier than 25.3.0.5525.
To determine whether a specific device is vulnerable, admins have to use the contentscannerstatus CLI command to check what version of Content Scanner Tools is running and inspect the “Enable File Reputation” checkbox under Mail Policies > Incoming Mail Policies > Advanced Malware Protection or Mail Policies > Outgoing Mail Policies > Advanced Malware Protection in the web-based management interface.
While the company didn’t share further details about attacks exploiting the CVE-2026-76519 flaw, it shared the indicators of compromise (IOCs) in the table embedded below.
| Log Message | Recommended Action |
|---|---|
| System Security: Suspected compromise indicator was found. Contact TAC for further recommendations. | Compromise detected. Follow the instructions in the Recommendations section of this Security Advisory |
| System Security: Security scan did not complete. Contact TAC for further recommendations. | Contact the Cisco Technical Assistance Center (TAC) for further support. |
| System Security: No compromise indicator was found. | No compromise detected. Upgrade to a fixed software release if applicable |
Cisco also warned customers to cross-check firewall and network logs for signs of suspicious activity (including downloads and uploads to and from external or suspicious IP addresses) because attackers may remove evidence of exploitation after gaining root-level command execution on vulnerable systems.
The company added that it has already deployed mitigations on cloud instances and contacted Cisco Secure Email Cloud device owners where it found evidence of a potential compromise.
“Cisco strongly recommends that customers who have been contacted restore a device to a secure configuration by renewing credentials and any cryptographic materials that are installed on the appliance, when possible. In addition, Cisco strongly recommends restricting access to the appliance and implementing robust access control mechanisms,” it said.
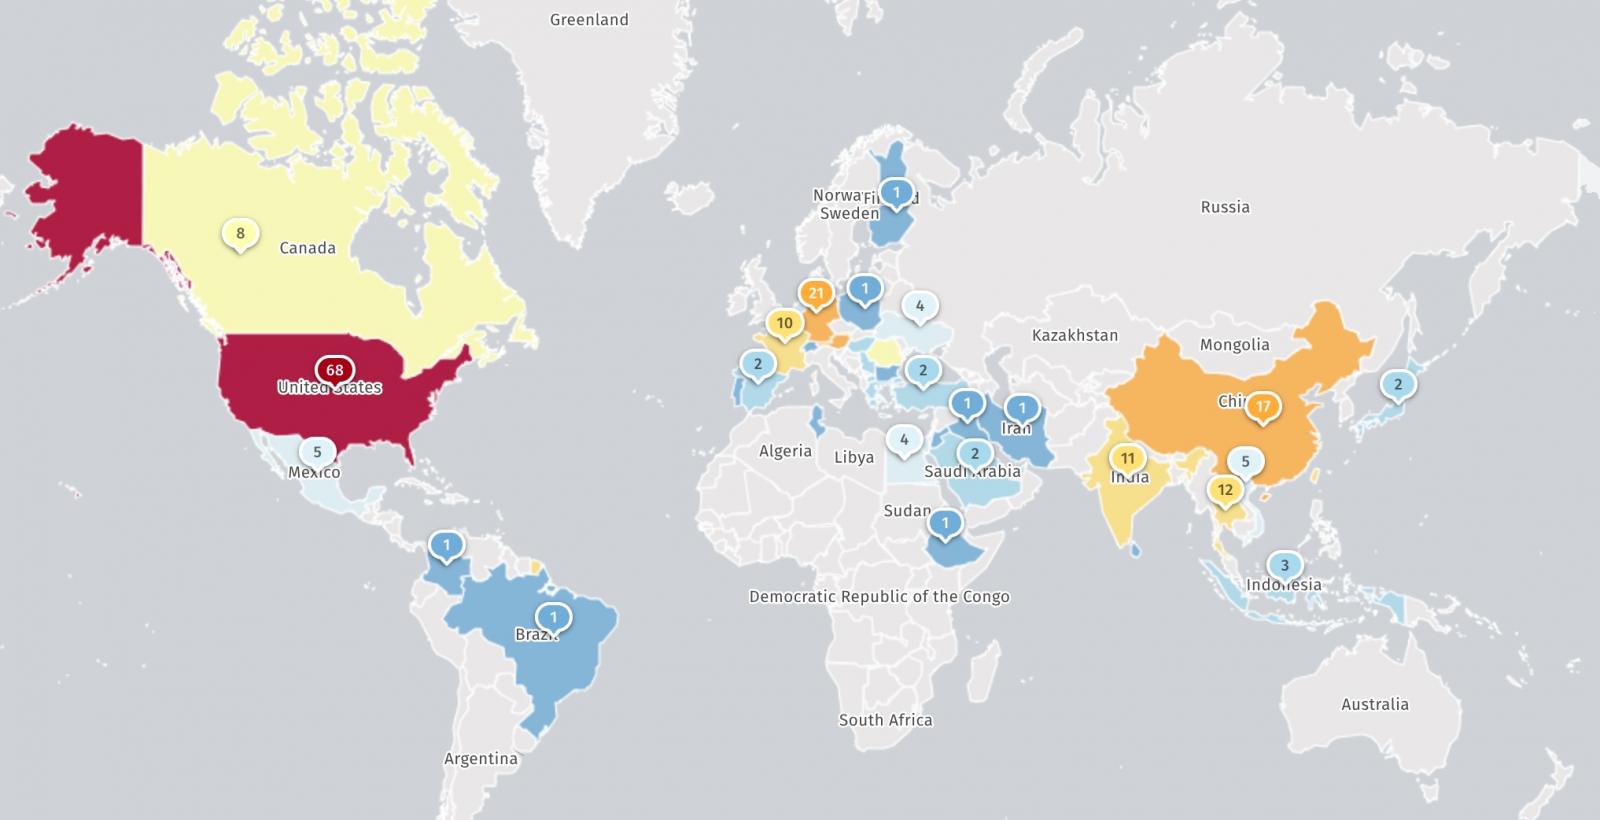
Internet security watchdog Shadowserver tracks nearly 300 Cisco Secure Email Gateway instances exposed online, but it provides no information on how many are honeypots or have already been secured.
Cisco addressed another critical SEG vulnerability (CVE-2024-20401) in July 2024 that lets attackers add new users with root privileges or permanently crash appliances using emails with malicious attachments.
In January, the company patched a maximum-severity Cisco AsyncOS flaw (CVE-2025-20393) that attackers have exploited in zero-day attacks targeting SEG and Secure Email and Web Manager (SEWM) appliances since November 2025.
More recently, last month, Cisco warned customers to patch a new actively exploited SEG zero-day (CVE-2026-76461) in the email parsing of Cisco AsyncOS Software that also lets unauthenticated, remote attackers execute arbitrary commands with root privileges on the underlying OS.
Since November 2021, the Cybersecurity and Infrastructure Security Agency (CISA) has added 100 Cisco vulnerabilities to its catalog of actively exploited flaws, seven of which have been abused in ransomware attacks.

Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.