

North Korean hackers are using a post-quantum cryptographic mechanism to secure malicious payload delivery in new operations that combine old and new malware.
The campaign targets South Korean organizations through a “rather complex” infection chain. Researchers at cybersecurity company Kaspersky dubbed the operation FlashHole and attributed it to the Lazarus Group.
Analysis of the malware revealed that the threat actor used the standardized ML-KEM post-quantum cryptographic mechanism to communicate with the command-and-control (C2) server for malware delivery.
Kaspersky says the attackers used LPEClient malware, previously associated with Lazarus, to receive ML-KEM-1024 public keys from its C2 infrastructure and generate shared keys that allowed it to decrypt subsequently incoming payloads.
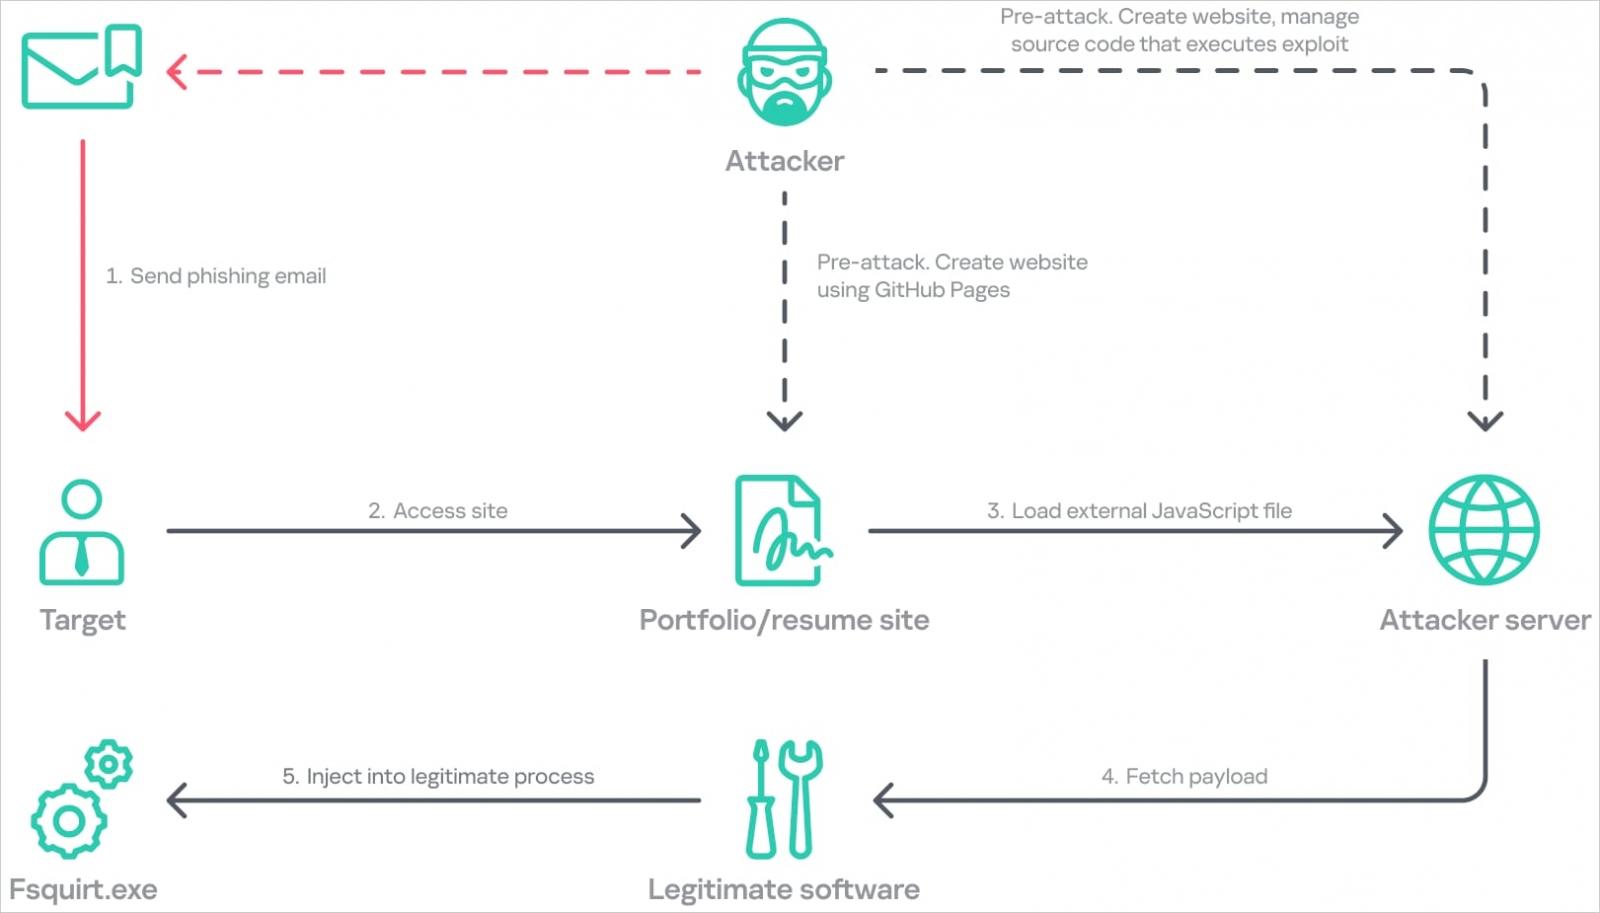
According to the researchers, the attacks started in July 2025 and relied on phishing pages directing targets to specially crafted GitHub pages.
Source: Kaspersky
These pages load JavaScript code from external domains, triggering an in-memory execution chain that involved INISAFE CrossWeb EX, a security tool popular in South Korea.
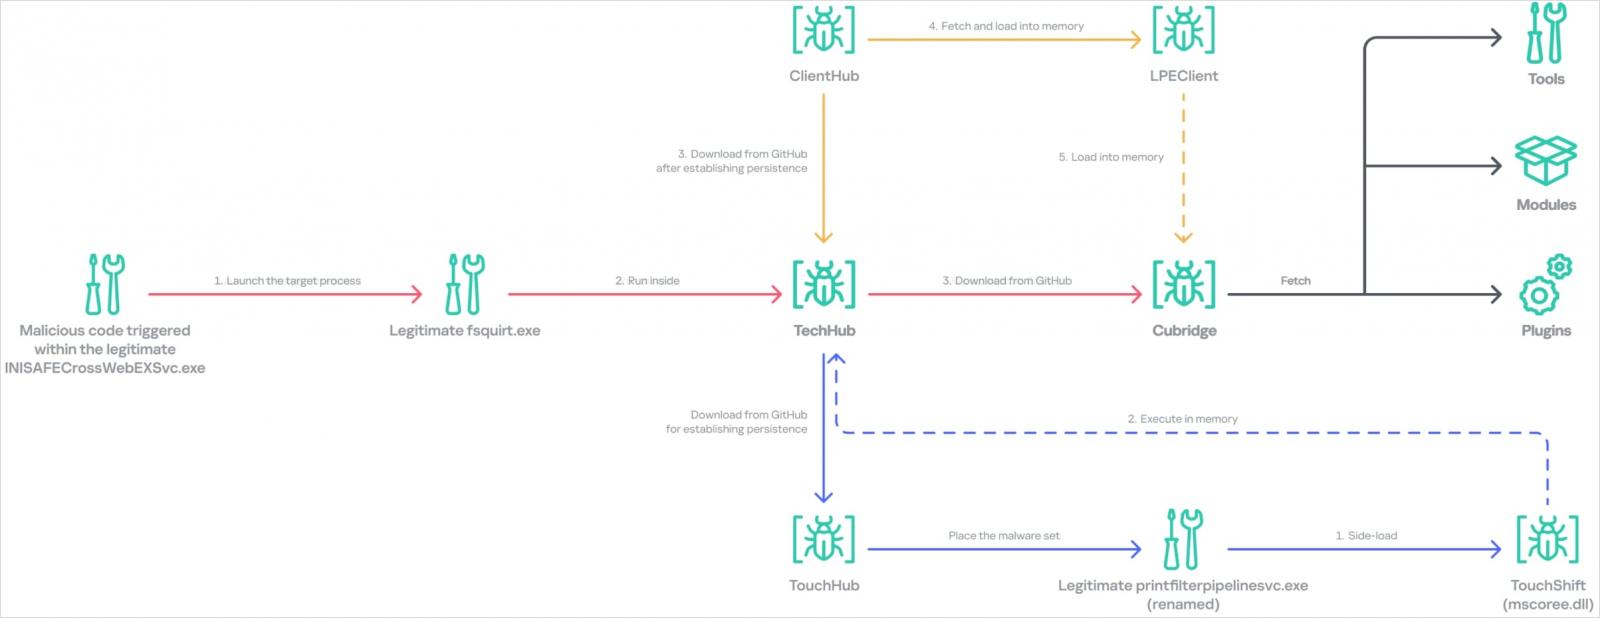
The security tool’s process executed the legitimate Windows binary fsquirt.exe, which was used to run shellcode that installed TechHub, a downloader responsible for retrieving additional malware from private GitHub repositories.
Source: Kaspersky
Kaspersky identified at least three companies in South Korea, in the software, construction, and wired communication equipment manufacturing sectors, but suspects that many more organizations were affected.
Another new tool seen in these attacks is ClientHub, a loader that supports Dropbox communications as well as direct data exchange with LPEClient.
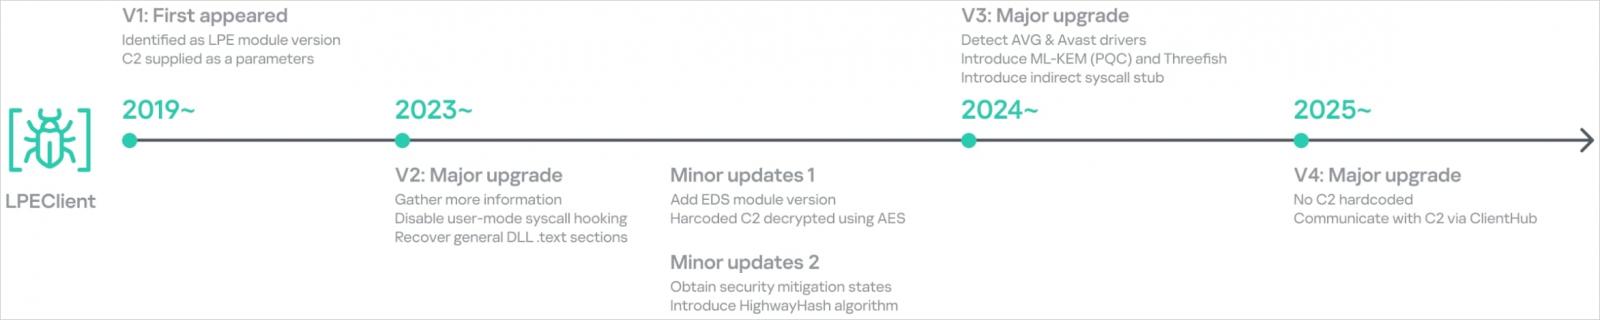
The researchers note that LPEClient profiles victims, receives encrypted payloads through ClientHub, and evades security monitoring.
Source: Kaspersky
Another malware observed in the attacks is Cubridge, a modular backdoor that provides file management, command execution, and reconnaissance capabilities, and also supports screenshot capturing and loading additional payloads on infected systems.
Kaspersky has also seen additional tools targeting Chromium-based browsers for account credentials, cookies, and browsing history.
The researchers note that most of Lazarus’ code runs in memory, though persistence mechanisms leave some files on the victim’s disk.
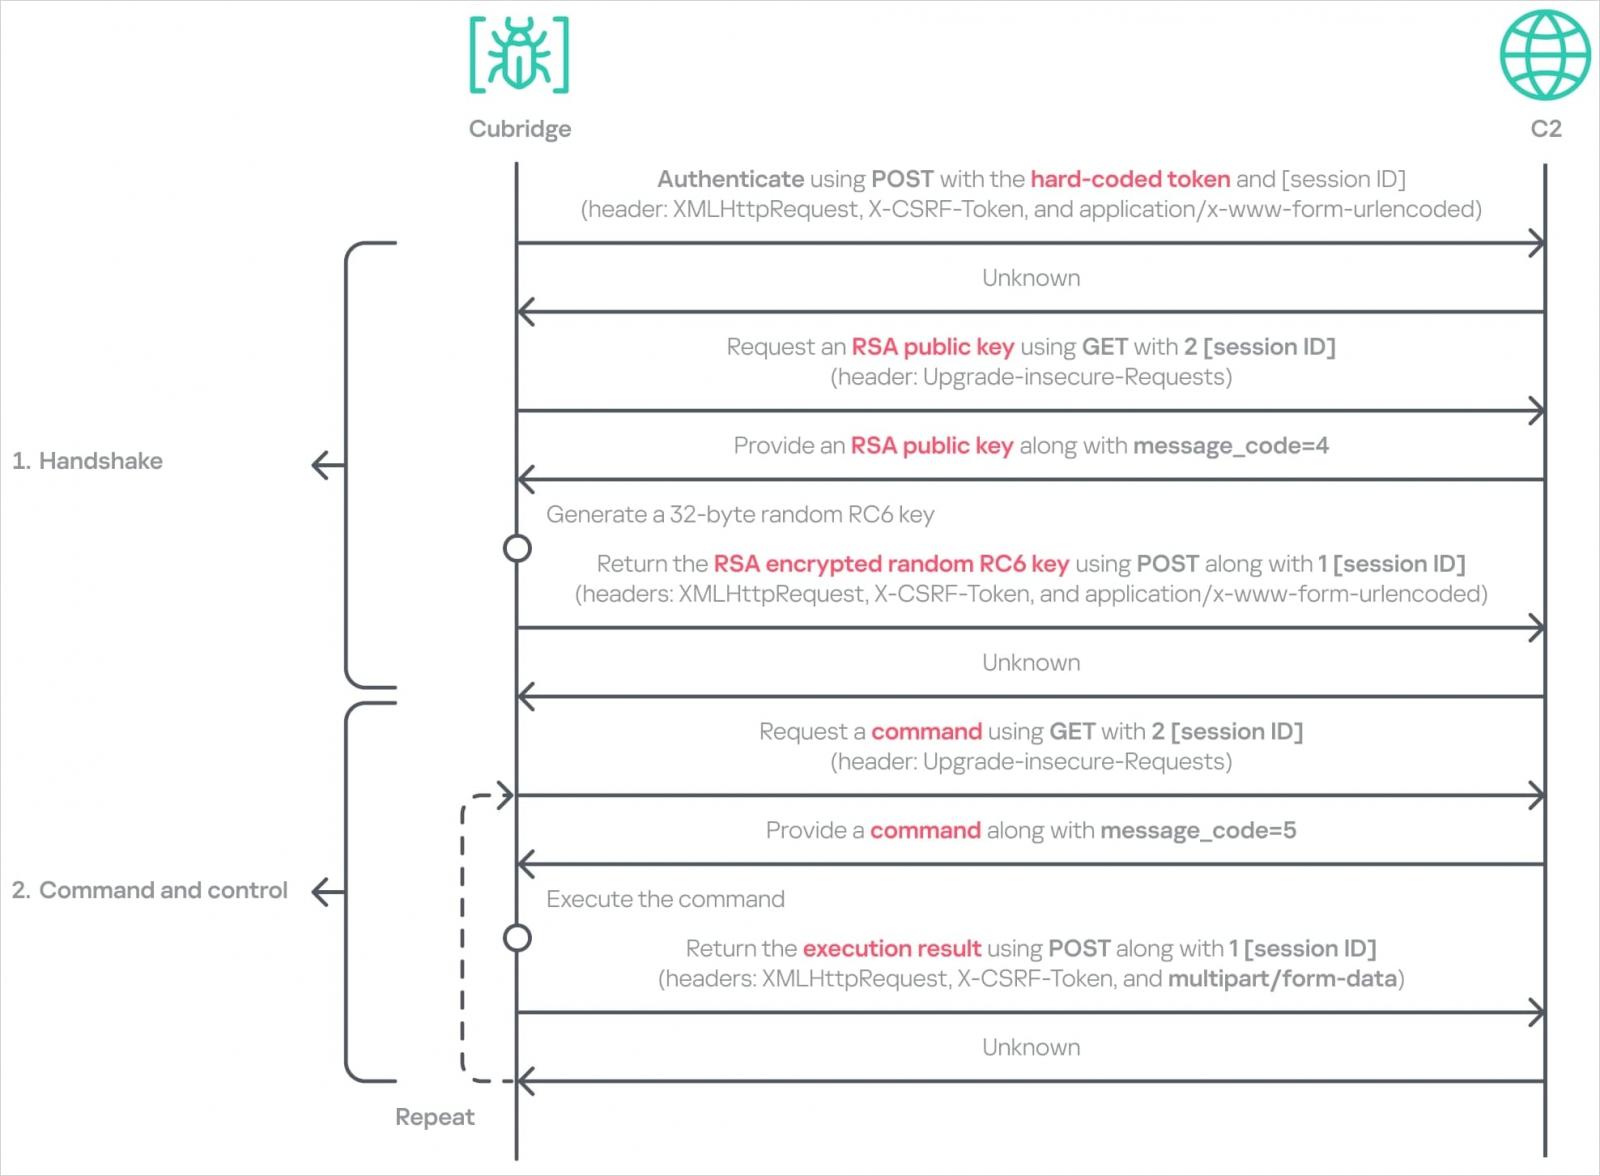
Source: Kaspersky
Post-quantum encryption
The use of the ML-KEM post-quantum cryptographic mechanism stands out in operation FlashHole since it is a NIST-approved standard present in multiple software projects as a way to protect data from “hack now decrypt later” attacks.
The technical analysis showed that LPEClient obtained from the C2 “a byte array comprising four 1,568‑byte blocks,” each containing an ML‑KEM‑1024 public key.
“LPEClient then generates four distinct pairs of shared keys and ciphertexts from these blocks, encrypts the ciphertexts with the GOST algorithm, and transmits them to the C2 server via ClientHub,” Kaspersky explains.
The shared secrets supply the key material for Threefish, another encryption algorithm, which decrypts the response containing parameters and an executable payload.
The final payload is Cubridge, which LPEClient reflectively loads into the host’s memory.
Kaspersky believes Lazarus uses this method along with an in-memory execution chain to lower detection risk to a minimum.
“The use of post-quantum cryptography shows that the group intends to hide subsequent payloads,” Kaspersky says.
Kaspersky researchers place FlashHole within the broader Cascade Hole activity and link it to the earlier Operation SyncHole with medium-to-high confidence.

Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.