
The PHP security team has shared mitigation measures for a new remote code execution vulnerability that affects systems with non-default configurations and has no patch.
PHP is an open-source web development language used by nearly 70% of all websites on the Internet. According to VirusTotal estimates, more than 5.1 million PHP hosts are exposed online, and roughly 3.8 million have at least one port open to attacks.
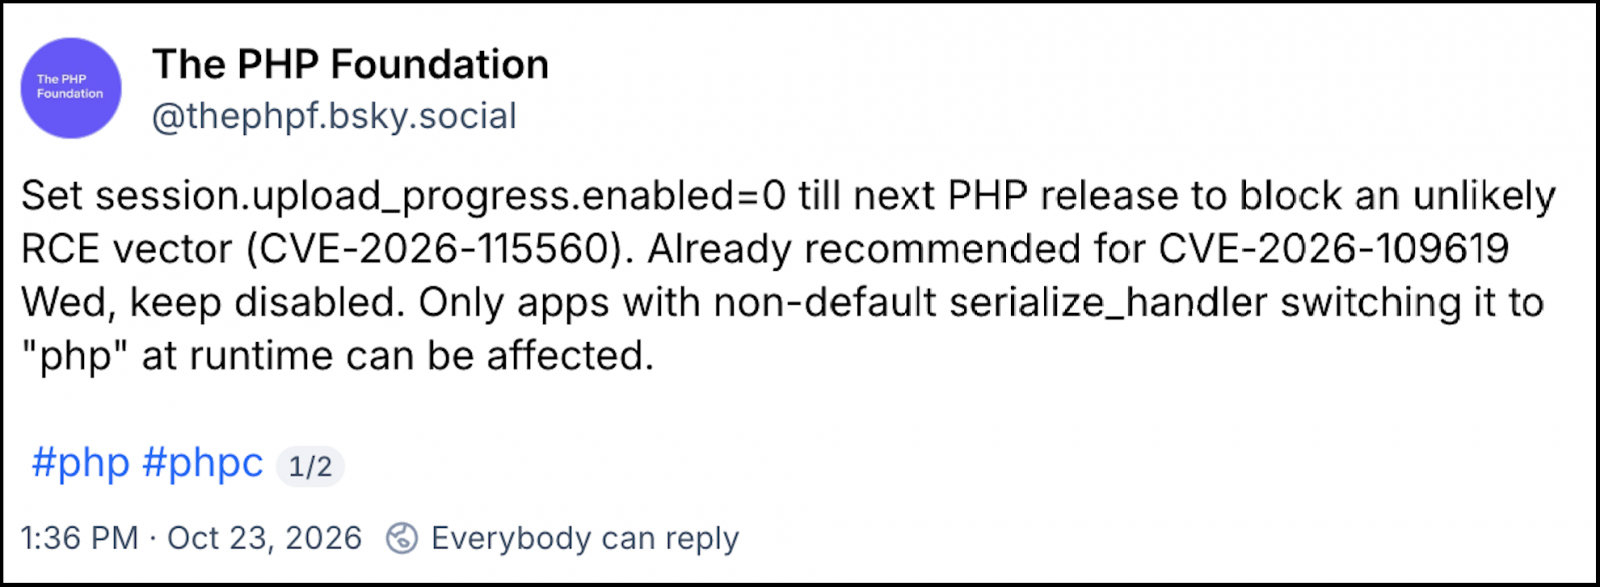
According to a Friday advisory, this security flaw (tracked as CVE-2026-115560) can only be exploited when targeting systems “with an unusual combination of configuration and application code.”
“An application must set session.serialize_handler to php_binary or php_serialize in its configuration and then switch it to php at runtime with ini_set() before calling session_start(). Session upload progress must also still be enabled,” the PHP team explained.
“Applications that never change the serialize handler at runtime can keep the feature enabled. Since this setup is unlikely in practice, we are handling it in the regular release cycle and will publish a full advisory for CVE-2026-115560 with the next release.”
Until a security patch is available, the PHP devs suggested setting session.upload_progress.enabled=0, adding that “If you applied it then, keep it in place and no further action is needed.”
This mitigation should have already been applied on Wednesday, before patching two other critical RCE vulnerabilities (CVE-2026-109618 and CVE-2026-109619) tracked collectively as PHP2Shell.
PHP2Shell flaws now targeted in attacks
The PHP security team patched the PHP2Shell vulnerabilities one day after urging admins to prepare to install the updates as soon as they became available.
While some proof-of-concept (PoC) code was published before the patches went live, the PHP security team said none were functional.
However, multiple cybersecurity companies (including Cloudflare, watchTowr, Previdian, Hadrian, and Patchstack) detected unsuccessful exploitation attempts before public disclosure, after some details on the PHP2Shell security flaws (including the CVE IDs and mitigation advice provided to some critical infrastructure providers) leaked online.
Security researchers at Amazon Threat Intelligence also said that attackers began targeting the PHP2Shell vulnerabilities four days before security patches were released on Wednesday.
“The actual payloads and choices in anonymization infrastructure varied, suggesting these were multiple actors. Technical analysis is ongoing, and it’s unclear if any of these attempts would have succeeded in real-world systems,” said AWS chief information security officer CJ Moses.
“PHP2Shell is now seeing broad exploitation attempts in the wild,” he added, though it’s unclear how many attacks (if any) have succeeded.
Dataminr’s Threat Research and Cyber Engineering (TRACE) team also said in a Thursday report that “observed activity since vulnerability disclosure remains limited to scanning, fingerprinting, and use of non-working exploits, with no known compromises,” but noted that “it remains only a matter of time for working POCs or successful exploitation activity to emerge.”

Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.