Skip to navigation Skip to content
  • contact@we-fix-pc.com
  • Facebook
  • Twitter
  • Linkedin
We Fix PC

We Fix PC

Computer Problems? We fix them all.

  • Home
  • About Us
  • Services
    • Data Recovery and Disaster Assessment
    • Full Hardware Diagnostics
    • Operating System and Software Installation
    • Networking and Wireless Troubleshooting
    • Malware Removal
    • Memory and Hard Drive Upgrades or Replacements
    • Parts Ordering and Installation
  • Blog
  • Contact Us
  • Managed Support Services
  • Remote Support
  • Domain & Hosting Services
    • Domain Check
    • Hosting Order
    • Certificates
    • Terms of Use
  • Premium Domains For Sale
  • Merger with Naples Geek Friend
  • Renew Request

Call Us

(239) 200-4849

Call Us Now

7963 Haven Dr. Unit 1
Naples FL 34104

Mon-Fri 8AM-6PM
Sat 8AM-5PM
Sun - CLOSED

We Fix PC

We Fix PC

Computer Problems? We fix them all.

Call Us

(239) 200-4849

Call Us Now

7963 Haven Dr. Unit 1
Naples FL 34104

Mon-Fri 8AM-6PM
Sat 8AM-5PM
Sun - CLOSED

  • Home
  • About Us
  • Services
    • Data Recovery and Disaster Assessment
    • Full Hardware Diagnostics
    • Operating System and Software Installation
    • Networking and Wireless Troubleshooting
    • Malware Removal
    • Memory and Hard Drive Upgrades or Replacements
    • Parts Ordering and Installation
  • Blog
  • Contact Us
  • Managed Support Services
  • Remote Support
  • Domain & Hosting Services
    • Domain Check
    • Hosting Order
    • Certificates
    • Terms of Use
  • Premium Domains For Sale
  • Merger with Naples Geek Friend
  • Renew Request

Tag: security

26 Sep

ShinyHunters uses WAF bypass trick in Oracle PeopleSoft attacks

The ShinyHunters extortion gang is using a URL-encoding trick to bypass web application firewall rules that mitigate the Oracle PeopleSoft CVE-2026-35273 flaw, allowing the threat actors to resume widespread exploitation of a flaw on vulnerable servers. Google’s Mandiant and Threat Intelligence Group (GTIG) say this new technique has allowed the threat actor to once again […]
An article by We Fix PC Posted in News
26 Sep

GitHub Actions re-enabled with Mini Shai-Hulud payload still active

Two third-party GitHub Actions previously compromised in a Mini Shai-Hulud campaign were re-enabled by their maintainer and remained accessible for more than a week despite still pointing to malicious code. After being compromised on May 18, the GitHub security team removed actions-cool/issues-helper and actions-cool/maintain-one-comment, preventing any downstream workflow from downloading malware. According to researchers at […]

An article by We Fix PC Posted in News
26 Sep

OpenAI’s AI agents accidentally uploaded user-provided images to third-party sites

OpenAI has confirmed it’s aware of a new security incident in which its AI agents uploaded user-provided images to third-party image-hosting services. OpenAI says most users were not affected, as it could only identify 53 incidents where agents accidentally uploaded images to the internet. The disclosure comes from OpenAI’s broader investigation into misaligned agent behavior […]

An article by We Fix PC Posted in News
25 Sep

Kiteworks urges 6-hour server shutdown over potential zero-day attacks

Secure file-sharing software company Kiteworks is urging customers worldwide to temporarily shut down their servers on Saturday for a six-hour window after receiving threat intelligence warning of a potentially imminent cyberattack. According to German technology publication Heise, Kiteworks CISO Frank Balonis emailed customers warning that the company had received “credible threat intelligence from law enforcement indicating […]

An article by We Fix PC Posted in News
25 Sep

ShinyHunters hacked Clop leak site using Grav CMS path traversal flaw

The Clop ransomware gang has moved its data leak site to a new Tor address after confirming its previous server was compromised and defaced through an unpatched Grav CMS flaw that BleepingComputer has learned is an unauthenticated path traversal vulnerability. The Clop leak site was breached earlier this month by the ShinyHunters extortion gang, which first uploaded a […]

An article by We Fix PC Posted in News
25 Sep

Elementor WordPress flaw lets attackers create admin accounts

A cross-site request forgery (CSRF) vulnerability in the Elementor plugin for WordPress could allow an unauthenticated attacker to create administrator accounts. Threat actors can exploit the flaw by tricking a logged-in administrator into opening a malicious link, causing the victim’s authenticated session to perform a REST API action permitted by their account. On default installations, […]

An article by We Fix PC Posted in News
25 Sep

CISA warns of Sharepoint, WSO2, Adobe Commerce flaws exploited in attacks

The Cybersecurity and Infrastructure Security Agency (CISA) warns that hackers are exploiting a critical authentication bypass vulnerability (CVE-2026-5430) affecting multiple products from enterprise software provider WSO2. The agency also added CVE-2026-71362, another critical-severity flaw affecting Adobe Commerce, to the list of security issues being leveraged in attacks. Hackers are also exploiting two additional vulnerabilities: a high-severity […]

An article by We Fix PC Posted in News
25 Sep

With the Rise of AI Agents, SOC 2 Should Adapt or Risk Irrelevance

Some compliance is mostly for show, and that’s being charitable. You go through it for the website badge, not to find weak spots in your organization. SOC 2 is not like that. There’s a reason your customers’ procurement teams demand it. They want to know whether they can trust you with their data, and SOC […]

An article by We Fix PC Posted in News
24 Sep

Exposed GitLab project email addresses let attackers push code

Private GitLab email addresses that allow developers to push issues or tasks to a project are being deliberately exposed in READMEs, contributing guides, and support pages used to collect bug reports. The addresses are part of a built-in GitLab feature called “Email work item to this project” and contain a long-lived token tied to the […]

An article by We Fix PC Posted in News
24 Sep

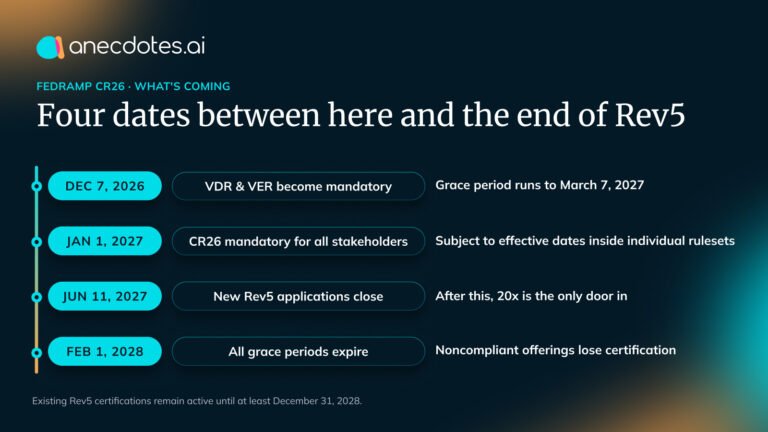
FedRAMP VDR & VER: Daily Scans Are Only the Beginning

If you hold a FedRAMP certification, the nearest deadline on your calendar is December 7, 2026. FedRAMP’s notice responding to CISA’s BOD 26-04 puts it plainly: “The Vulnerability Detection and Response rules will be mandatory for all cloud service offerings obtaining or maintaining FedRAMP Certification effective December 7, 2026,” with a grace period through March […]

An article by We Fix PC Posted in News

Posts pagination

Previous page Page 1 … Page 3 Page 4 Page 5 … Page 806 Next page

Recent Posts

  • ShinyHunters hacker reportedly detained in Jordan, aiding FBI
  • Danish university DTU breach exposes data of up to 200,000 people
  • Frontline Education breach exposes school district employee data
  • Warlock ransomware breach SharePoint in water, telecom operator attacks
  • GitLab warns of critical RCE vulnerability in AI Gateway service

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • August 2025
  • November 2024
  • October 2024
  • September 2024
  • August 2024
  • July 2024
  • June 2024
  • May 2024
  • April 2024
  • March 2024
  • February 2024
  • January 2024
  • December 2023
  • November 2023
  • October 2023
  • September 2023
  • August 2023
  • July 2023
  • June 2023
  • May 2023
  • April 2023
  • March 2023
  • February 2023
  • January 2023
  • December 2022
  • November 2022
  • October 2022
  • September 2022
  • August 2022
  • July 2022
  • June 2022
  • May 2022
  • April 2022
  • March 2022
  • February 2022
  • January 2022
  • December 2021
  • November 2021
  • October 2021
  • September 2021
  • August 2021
  • July 2021
  • June 2021
  • May 2021
  • April 2021
  • March 2021
  • February 2021
  • January 2021
  • December 2020
  • November 2020
  • October 2020
  • September 2020
  • August 2020
  • July 2020
  • June 2020
  • May 2020
  • April 2020
  • March 2020
  • February 2020
  • January 2020
  • December 2019
  • November 2019
  • October 2019
  • September 2019
  • August 2019
  • July 2019
  • June 2019
  • May 2019
  • April 2019
  • March 2019
  • September 2017
  • August 2017
  • contact@we-fix-pc.com
  • Facebook
  • Twitter
  • Linkedin
Computer Repair Logo

Whether you need a quick repair or a complete rebuild of your computer, laptop, tablet or phone, We-Fix-PC is here to help. We have all the best and latest technologies on the market and we use them to bring you quality services and more than 20 years of experience that you always wanted.

Our Services

  • Full Hardware Diagnostics
  • Parts Ordering and Installation
  • Data Recovery and Disaster Assessment
  • Memory and Hard Drive Upgrades or Replacements
  • Operating System and Software Installation
  • Network and Wireless Troubleshooting
  • Malware Removal
  • Managed Support Services

Contact Information

  • 7963 Haven Dr. Unit 1
    Naples FL 34104
  • (239) 200-4849
  • contact@we-fix-pc.com

Our Newsletter

Business Hours

  • Monday 8:00AM - 6:00PM
  • Tuesday 8:00AM - 6:00PM
  • Wednesday 8:00AM - 6:00PM
  • Thursday 8:00AM - 6:00PM
  • Friday 8:00AM - 6:00PM
  • Saturday 8:00AM - 5:00PM
  • Sunday Closed
Copyright © 2002 - 2026 Powered by We Fix PC Tech & Computer Repair | All Rights Reserved | Website Designed and Developed by We-Fix-PC Tech & Computer Repair & Web Design
Scroll to top

Ernani here, feel free to ask me any questions!