

The ShinyHunters extortion gang breached the Clop (aka Cl0p) ransomware operation’s data leak site, defacing the Tor site and allegedly stealing server data and the private keys for its onion service.
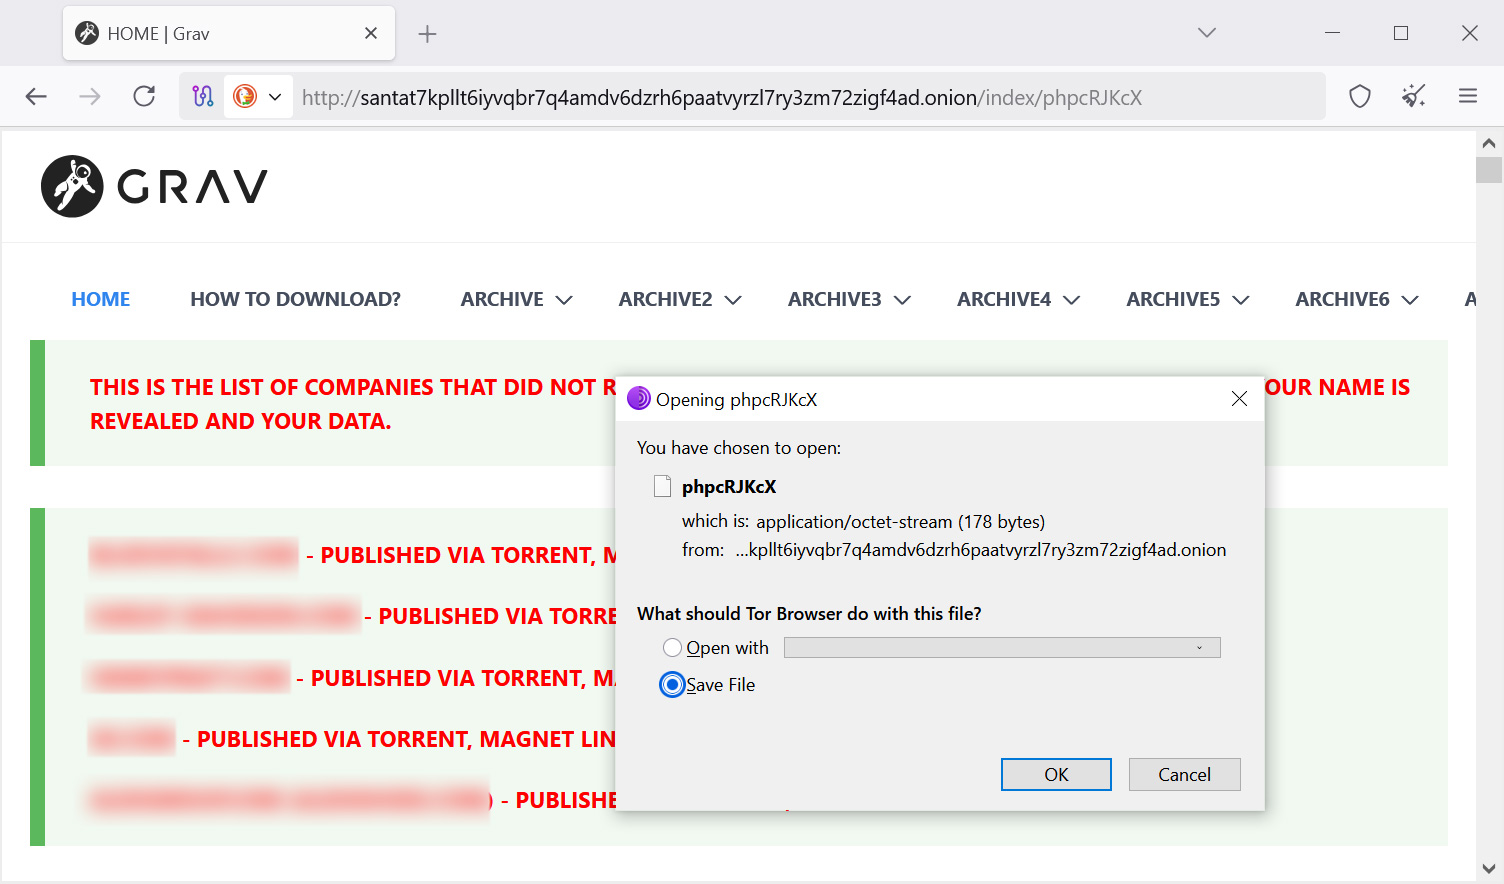
The attack began Friday night when ShinyHunters exploited what they claim is an unauthenticated file upload vulnerability in Grav CMS, which they used to upload a small text file to Clop’s site.
Source: BleepingComputer
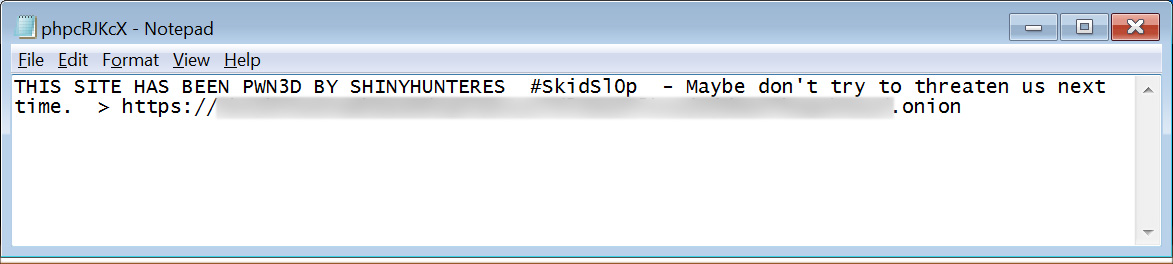
The small text file contained a message from the threat actors to the Clop ransomware gang, warning not to threaten them and including a link to ShinyHunter’s own data leak site.
“THIS SITE HAS BEEN PWN3D BY SHINYHUNTERES #Skids10p – Maybe don’t try to threaten us next time,” read the uploaded file.
Source: BleepingComputer
The file also contained a link to the ShinyHunters data leak site.
BleepingComputer confirmed that the file had been uploaded to Clop’s server and could be downloaded directly from the ransomware gang’s Tor site.
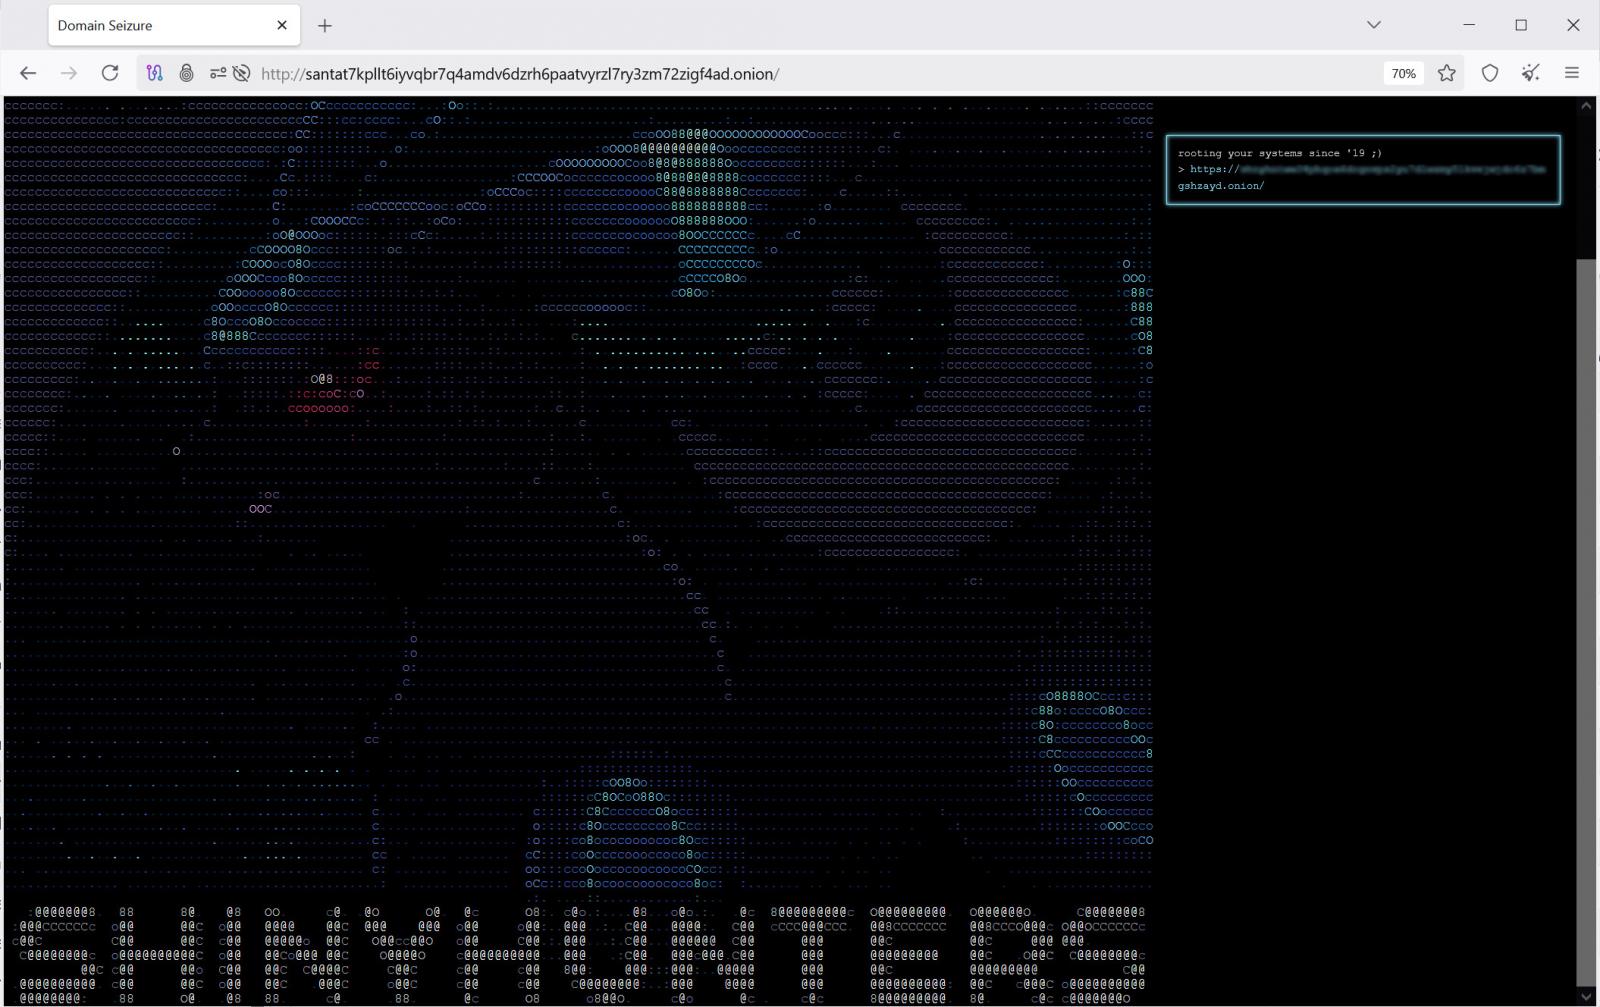
Several hours later, ShinyHunters told BleepingComputer that they had “completely defaced” the Clop site.
Visiting the site confirmed it had been replaced with a page displaying ASCII art of Umbreon, the Pokémon used as ShinyHunters’ logo. The defacement also included a link to the group’s Tor site and the message, “rooting your systems since ’19 ;)”.
Source: BleepingComputer
At the time of this writing, the defaced page is still being served from Clop’s infrastructure, according to ShinyHunters.
ShinyHunters claims data theft
ShinyHunters told BleepingComputer it gained “full access” to the server and stole source code, Grav CMS plugins, system logs, and other data.
“The data we stole includes source codes, gravCMS plugins, and other things. We are still downloading and reviewing them,” ShinyHunters told BleepingComputer.
The threat actors also claim to have stolen all files stored under /var/log, which could contain system activity, authentication logs, and potentially, the IP addresses of those who connected to it.
ShinyHunters also claims to have obtained the private keys used by Clop’s Tor onion service.
“We have their onion keys. So if they kick us out it wouldn’t matter at all because we control the private keys to host the same exact onion URL,” the threat actor claimed.
If the keys are valid, it would allow the threat actors to operate a Tor site using Clop’s existing onion address on servers they control.
BleepingComputer has independently confirmed the defacement and earlier uploaded file but has not independently verified ShinyHunters’ claims that it stole server logs, source code, or Clop’s onion private keys.
ShinyHunters says it is now reviewing the allegedly stolen data.
When asked what they planned to do with the stolen information, the threat actor responded, “Going to extort them.”
The group says it plans to publish a message on its own leak site instructing Clop to contact them within 72 hours.
Cybersecurity researcher VXDB told BleepingComputer the Umbreon artwork now displayed on Clop’s leak site is the same as what was used in the August 2020 defacement of the HackForums website, which ShinyHunters also claimed at the time.
Feud between cybercrime groups
ShinyHunters says the attack is retaliation for threats allegedly made by a Clop representative during an ongoing feud between the cybercrime groups.
According to ShinyHunters, a Clop representative threatened to identify group members and made violent threats after ShinyHunters disrupted a Clop data theft campaign.
ShinyHunters says the dispute dates back to Clop’s 2025 Oracle E-Business Suite data theft campaign.
In October 2025, Clop exploited multiple vulnerabilities in Oracle E-Business Suite servers, including a zero-day flaw tracked as CVE-2025-61882, to steal data from organizations in extortion campaigns.
Around the same time, threat actors calling themselves “Scattered Lapsus$ Hunters,” including ShinyHunters, leaked a proof-of-concept exploit that Oracle later confirmed matched an exploit used in the Clop attacks.
At the time, ShinyHunters told BleepingComputer the exploit had originally belonged to them and that Clop obtained it without authorization.
ShinyHunters claims that tensions escalated after the Oracle campaign, with a Clop representative allegedly threatening members of the group.
“During the Oracle EBS campaign they ran and stole from me last year, someone from cl0p personally messaged me and said, and I quote (translated from Russian): I have more money than you and all of your people combined, I’ll kill you soon,” ShinyHunters told BleepingComputer.
BleepingComputer has not independently verified these allegations and has contacted Clop about the breach and the allegations made by ShinyHunters and will update the story if we receive a response.

Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.