
A new Windows malware named ClosedQuorum uses Google Gemini, DeepSeek, Qwen, and Mistral AI models to autonomously determine the actions to take during post-compromise stages of an attack.
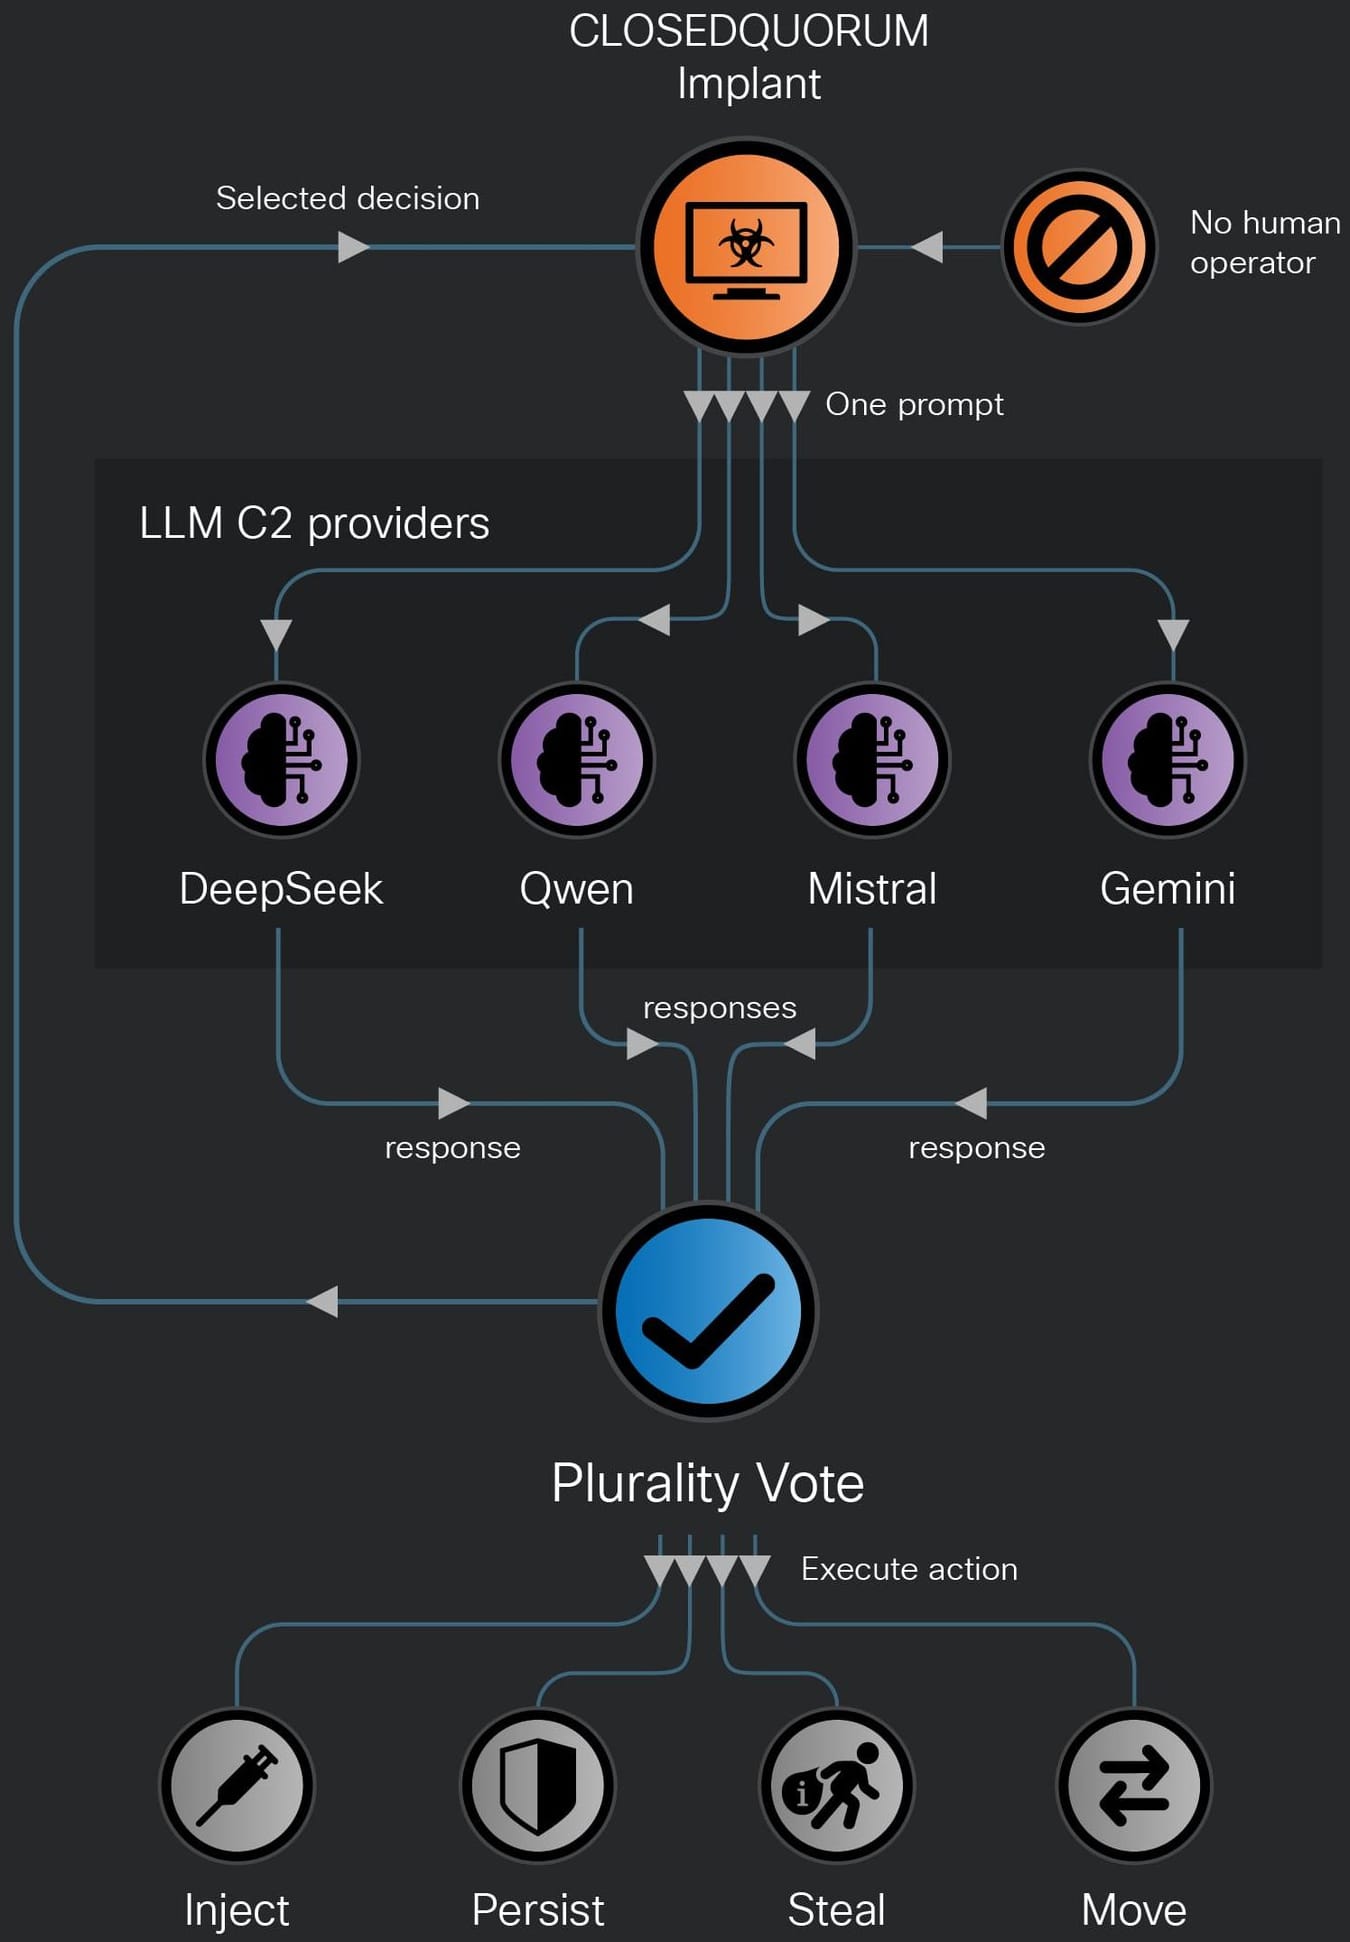
The Go-based malware acts with no commands from a human operator, using reconnaissance information and a voting system to decide its next step on infected hosts.
When votes are tied, DeepSeek has priority at making the final call, based on the option it considers most appropriate, followed by Qwen, Mistral, and Gemini.
Cisco Talos researchers analyzing ClosedQuorum say that the models are restricted to a predefined set of decisions, including:
- steal — simultaneously runs LSASS credential dumping, browser (Chrome, Edge, Firefox) credential theft, and cryptocurrency-wallet (MetaMast, Exodus, Ethereum) extraction
- inject — generates shellcode, then uses either process hollowing or Early Bird APC injection
- persist — executes the malware’s persistence module
- move — included as a possible lateral movement decision, but the analyzed distribution build has no corresponding handler, so it cannot execute this action
The stolen details are then passed to the operators via a Discord webhook, so apart from the malware delivery, the attack can be fully automated.
Source: Cisco
Talos describes ClosedQuorum as the first publicly documented Windows implant to delegate tactical command-and-control (C2) decisions to a panel of AI models, commenting that this adds greater speed and scaling potential to malicious operations.
The researchers also highlight that this eliminates human interaction, allowing the attack chain to proceed at any time.
However, Cisco notes that this may also pose challenges in certain cases where rate limits are hit, output is malformed, or commercial APIs that the system relies on are temporarily unavailable.
Since it is not a sophisticated piece of malware, it is unclear if ClosedQuorum is a test or experiment. However, the researchers warn that it represents an “architectural shift towards attack-chain automation.”
“While we do not have confirmation of in-the-wild deployment, artifacts from the binary were used to connect the developer to postings on criminal forums related to carding, dating back to 2025,” explains Cisco Talos.
The binary that Cisco Talos analyzed contains placeholder API credentials and a dummy Discord webhook, although the creators can add those in their custom ClosedQuorum builds.
Cisco Talos discovered ClosedQuorum through CAIRN, an open-source toolkit it released to help researchers track and analyze AI-integrated malware.

Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.